

Protecting SSH from Password Brute-Force Attacks with Fail2ban
To protect your server from brute-force attacks, where attackers try to crack passwords by trial and error, it is preferable to set up and use key-based authentication instead of password authentication.
Another protection method is to use Fail2ban. Fail2ban analyzes the logs of services running on the server and, when it detects suspicious activity, blocks the IP addresses of potential attackers. Fail2ban can be used to protect various services, such as Apache, FTP, dovecot and others.
In this article, we will look at a basic Fail2ban setup to protect the SSH service from password brute-force attacks.
To install Fail2ban on Ubuntu/Debian, run the following:
sudo apt updatesudo apt install fail2ban -yTo install it on CentOS:
sudo yum update && yum install epel-releasesudo yum install fail2banAdd Fail2ban to the list of programs that start at system boot:
sudo systemctl enable fail2banOn Ubuntu, SSH protection is enabled automatically after Fail2ban is installed. By default, Fail2ban bans an IP address for 10 minutes if 5 failed authentication attempts are recorded within 10 minutes.
Other parameters of the tool can be changed in its settings.
Fail2ban Configuration File
Fail2ban settings are stored in the /etc/fail2ban/jail.conf configuration file.
The settings are divided into sections. The [DEFAULT] section contains general parameters that define how Fail2ban works as a whole and apply to most services. Parameters for a specific service are set in the corresponding section (for example, [sshd], [apache-auth], [vsftpd]).
It is recommended not to change parameters directly in the jail.conf file. Instead, create a new jail.local file in the same directory.
You can make a copy of the original file (this is convenient if you plan to configure Fail2ban to protect several services, not just SSH):
sudo cp /etc/fail2ban/jail.conf /etc/fail2ban/jail.localOr you can create an empty file with this name and add the parameters you need:
sudo touch /etc/fail2ban/jail.localIn the new file, you only need to specify the settings whose values you want to change. For all other parameters that you do not specify explicitly, Fail2ban will use the default values.
Configuring SSH Protection
Open the jail.local file for editing:
sudo nano /etc/fail2ban/jail.localHere is an example of settings you can add to the file:
[DEFAULT]
ignoreip = 95.111.123.21

[sshd]
enabled  = true
findtime = 120
maxretry = 3
bantime = 43200
These settings mean that if 3 failed login attempts are made from any IP address, except the one specified in ignoreip, within 2 minutes, Fail2ban will ban that address for 12 hours.
The DEFAULT section can contain parameters such as the ban period (bantime), the number of attempts (maxretry) and so on. However, in this guide, we will define most settings in a separate section for SSH and specify only the ignoreip parameter in the DEFAULT section.
The ignoreip parameter is a "whitelist" of IP addresses that will not be banned after failed connection attempts. You can specify your own IP address (if it is static) or the addresses you connect to the server from. You can specify several addresses separated by spaces, or a subnet mask.
If you are not going to use a "whitelist", you can simply comment out the line by adding the # character in front of it.
The [sshd] section contains settings for how Fail2ban works with a specific service, SSH. Note that, depending on the system, this section may be called [sshd], [ssh] or [ssh-iptables] (you can check this in the jail.conf file).
As mentioned earlier, if a parameter is missing from the file, Fail2ban will use the default value. Therefore, you only need to specify the settings whose values you want to change.
The settings above specify the following parameters:
-
enabled: This required parameter determines whether the section is enabled. To enable the section, the value must be true (the default). Note that on CentOS this parameter may be commented out by default. If you are editing a copy of the main jail.conf file, make sure this line is uncommented (the # character is removed) to activate the section.
-
bantime: This parameter sets the ban duration in seconds, that is, the period of time for which a suspicious IP address will be banned.
-
maxretry: This parameter sets the number of failed attempts within the findtime period after which a ban is applied.
-
findtime: This parameter sets the period of time in seconds within which an action (in this case, a failed connection attempt) must be repeated a certain number of times (maxretry) for a ban to occur.
In addition, these settings can include other parameters, such as:
-
port: The port used by the service, in this case SSH. If SSH uses a non-standard port (not 22), it must be specified here. If the port is standard, this parameter is optional.
-
logpath: The path to the log file that Fail2ban analyzes. By default, this is the standard path to the sshd log.
-
action: The action performed when an IP address is banned. By default, a suspicious IP is blocked by modifying iptables rules.
To block all ports completely for a given IP, you can use: action = iptables-allports. If the server uses firewalld or ufw, you can set the corresponding value for the action parameter, such as firewallcmd-ipset or ufw.
To view the contents of the /etc/fail2ban/action.d directory, you can use the command:
ls /etc/fail2ban/action.dThis will show you all available Fail2ban action configuration files.
After making changes to the file, save it. Then restart Fail2ban:
sudo systemctl restart fail2ban.service
Verification
After configuring Fail2ban, you should check that it works. It is best to do this not immediately, but a few hours after saving the settings, to get more meaningful results.
To view the list of banned IP addresses, you can use the iptables command:
sudo iptables -L
You can also view the Fail2ban logs:
sudo tail /var/log/fail2ban.log 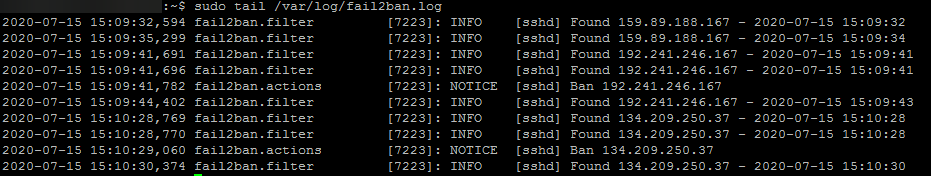
You can also get information about the status and activity of Fail2ban through its client interface:
sudo fail2ban-client status sshd
These steps will help you make sure that the Fail2ban protection you have configured is working and effective.

